AI-generated illustration. AI-assisted changes need approval tied to a defined scope, accountable owners, and evidence of cross-request behavior, not merely a plausible patch.
Approve AI-assisted changes to account-abuse controls only within a defined risk tier, with a named engineering owner and evidence covering behavior across requests. Changes to identifier correlation, retained activity, or blocking decisions need security approval before release, plus privacy review when identifier handling or retention changes.
The boundary is not whether an AI tool can produce a plausible patch. It is whether the team can explain and verify how the patch connects past activity to the next account decision.
Why stateful controls need a different review boundary
Cloudflare’s supplied announcement excerpt describes a new Account Abuse Protection dashboard using stateful analysis and edge-generated Hashed User IDs to help investigate and block account abuse. Cloudflare also says fraudsters increasingly use AI to bypass stateless checks. These are publisher claims: the excerpt does not independently establish that trend, demonstrate the dashboard’s effectiveness, or describe its development practices. See Cloudflare’s account-abuse dashboard announcement.
For engineering leaders, the review implication is narrower: a small code change can alter a security decision by changing which earlier requests still count.
A stateless check evaluates the current request. A stateful control can also consider related earlier activity, its association with an identifier, and whether that history should still influence a decision. Reviewing one request in isolation cannot establish that those relationships remain correct.
Classify the behavior changed, not the file edited
Use this matrix as an internal policy template. Assign the highest tier a patch touches. If its effect is unclear, the owner must trace the data and decision paths before classifying it as display-only.
“Permitted assistance” means assistance within the approved development environment. It does not authorize access to production credentials or live customer data.
| Change tier | Permitted AI assistance | Accountable owner | Required release evidence | Release authority |
|---|---|---|---|---|
| 1. Display-only: labels, layout, or formatting that cannot change evidence meaning, access, or enforcement | Draft UI changes and presentation tests | Dashboard engineering owner | Diff review; confirmation that queries, identifier exposure, ordering, timestamps, decision inputs, and action bindings are unchanged | Designated engineering reviewer |
| 2. Investigation semantics: aggregation, filtering, or presentation that changes how an analyst interprets activity | Draft transformations and synthetic investigation fixtures | Investigation workflow owner | Trace from stored events to displayed conclusions; sequences covering missing, expired, and reordered events; review of resulting analyst actions | Engineering owner and security reviewer; privacy reviewer if visibility or identifier handling changes |
| 3. Identity and state lifecycle: identifier derivation, linking, rotation, retention, or expiry | Propose designs, patches, and synthetic tests; no tool-controlled release | Control service owner | Identifier lifecycle specification; cross-request tests; retention and deletion evidence; compatibility and state-aware rollback plan | Engineering owner, security approver, and privacy reviewer |
| 4. Enforcement: thresholds, blocking, challenges, recovery, or failure behavior | Draft candidate changes and tests in isolation; release requires separate authorization | Enforcement service owner | Tier 3 evidence where applicable; allow/block boundary tests; legitimate-use sequences; failure-mode analysis; bounded rollout and recovery plan | Engineering owner and security approver; privacy review for identifier or retention changes; named release authority |
A patch can touch several tiers. Extending retention is a lifecycle change; if retained events feed a blocking threshold, it also changes enforcement. Nor is every dashboard edit low risk. Changing timestamp interpretation or hiding an identifier reset can change an investigation without modifying a blocking function.
One person may hold several roles in a small team. Still, the decision record should distinguish engineering correctness, security acceptance, privacy acceptance, and release authorization. The AI tool cannot own those decisions.
Require evidence about the identifier’s whole lifecycle
Require a short cross-request behavior contract before approval. The patch owner should answer:
- Identity: What does the identifier represent: an account, session, device, or another entity? When can distinct activities share it?
- Boundaries: Which tenant, account, and environment boundaries must correlation never cross?
- Transitions: What happens on logout, credential reset, identifier rotation, account deletion, or changes to identifier inputs?
- Time: When does activity stop affecting decisions? When is it physically deleted? Does new activity extend the life of earlier activity?
- Decision: Which events count, and what happens exactly at an expiry or threshold boundary?
- Failure: What happens if state is unavailable, stale, duplicated, or delivered out of order?
- Recovery: What state remains after rollback, and how will it be handled safely?
This contract exposes the assumptions tests must exercise. “The tests pass” is not a substitute.
Hashing does not establish anonymity. An identifier can link activity across requests without displaying the underlying account value. Review derivation, linkability, access, and retention separately.
Also separate decision expiry from storage deletion. A record may stop counting toward blocking while remaining stored. Evidence for one does not establish the other.
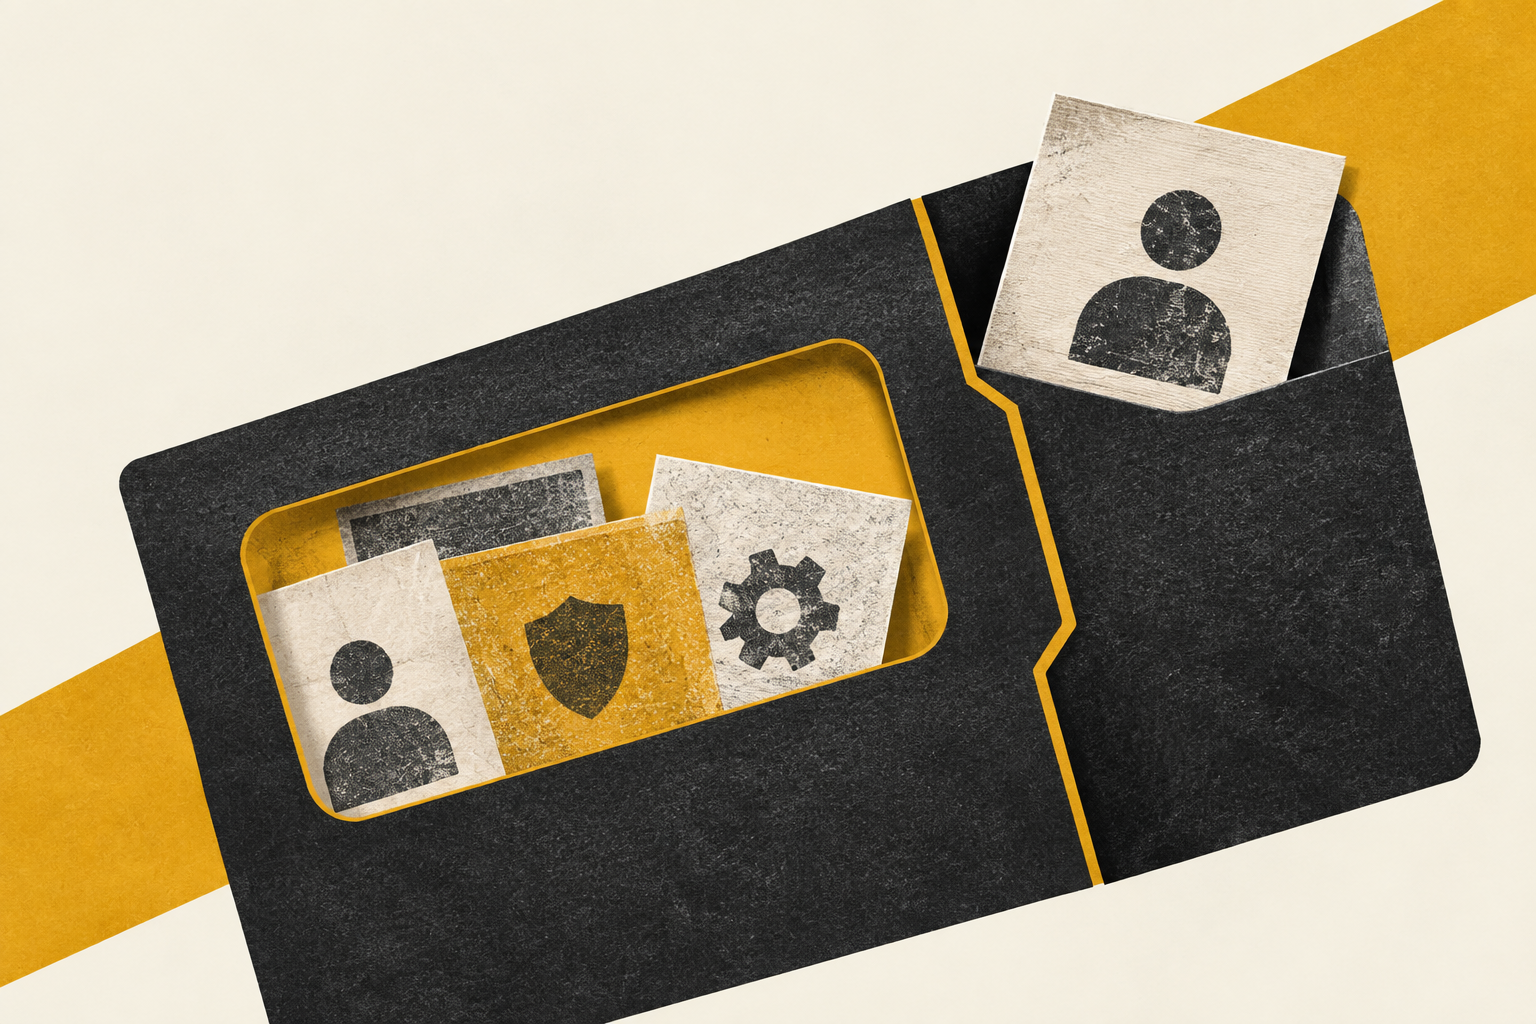
AI-generated illustration. Conceptually, the window represents activity eligible to influence a decision; the pocket represents stored history. An event can stop counting toward a block without being deleted.
Worked example: extending failed-login history
Consider a hypothetical AI-assisted patch with these explicit assumptions:
- Failed-login events are associated with an account-scoped identifier within one tenant.
- The fifth failed login inside a rolling lookback window triggers a block.
- The existing decision window is 15 minutes; the patch proposes 60 minutes.
- Each event expires individually from that window. New activity does not refresh older events.
- Some accounts legitimately have multiple authorized users.
- Evaluation uses synthetic identities and an isolated state store.
The patch may look like a configuration change. It changes enforcement.
For failures at minutes 0, 10, 20, 30, and 40, the decision at minute 40 sees only the failures at minutes 30 and 40 under the 15-minute window. Under the proposed 60-minute window, it sees all five and blocks. This calculation demonstrates changed behavior under the assumptions, not successful abuse prevention.
Assign the control service owner to explain the change, a security approver to accept its enforcement consequences, and a privacy reviewer to assess the longer use of linked activity. The packet must also establish whether storage retention changes: a longer decision window alone does not answer that question.
Evidence the review packet must contain
| Synthetic sequence | What reviewers need to establish |
|---|---|
| The five failures above | The longer window changes the decision intentionally |
| Events immediately before, at, and after expiry | The exact time-boundary rule is specified and implemented consistently |
| A failed request just before an older event expires | New activity does not extend the older event’s life |
| Identifier rotation between failures | History follows the approved identity policy, without silent loss or duplication |
| Similar identifiers in different tenants | Activity never crosses the specified tenant boundary |
| Two authorized users sharing an account, with one mistyping a password | The team understands who may be blocked and accepts the recovery path |
| Duplicate, delayed, and out-of-order events | Counts and expiry follow a documented policy |
| Rollback after state accumulates under the longer window | Restoring the old code restores the intended decision behavior and addresses retained data |
Expected outcomes must come from the approved contract. An AI-generated implementation and AI-generated tests can share a mistaken assumption. Agreement between them is not enough: a human reviewer must validate the expectations, especially for identity transitions and legitimate shared-account behavior.
Make a release decision, not just a code-review decision
Suppose the hypothetical packet contains code and a single-request test, but no sequence-test results, privacy decision, or retained-state rollback plan.
- Hold production release. The packet does not establish the changed cross-request behavior or provide the required approvals.
- Restrict further work to isolated evaluation. AI assistance may continue on the design, fixtures, and candidate patch without expanding access or deployment scope.
- Reconsider approval after the missing evidence and signoffs arrive. Name the permitted scope and rollout conditions; do not grant blanket permission for future changes.
This is an evidence gap, not proof that the patch is defective. A plausible patch is no reason to waive missing evidence.
Rollback must include state, not just code
Reverting a commit may leave behind identifiers, counters, events, or block records created under the new rules.
Require the rollback plan to answer three questions:
- Can the previous version interpret the new state safely? If not, define a compatible migration or a separate, versioned state path that can be tested.
- What happens to activity retained longer than the old policy allowed? Name the owner, deletion or expiry procedure, and verification evidence.
- What happens to decisions already issued? Explain whether blocks persist, how legitimate access can be restored, and which approved behavior applies if state becomes unavailable.
Do not default to clearing all state. That could erase information the control needs. Rehearse recovery only against isolated test resources, and verify that the restored system uses the intended decision window.
Record permission as a bounded decision
A reusable approval record can be this short:
Scope: Named control, environment, and behavior change.
Risk tier: Highest affected tier, with rationale.
Owners: Engineering owner, security approver, privacy reviewer where applicable, and release authority.
Evidence: Behavior contract, independently reviewed expectations, sequence-test results, and state-aware rollback evidence.
Decision: Approve within stated bounds, restrict to evaluation, or hold release.
Expansion condition: Evidence and approvals needed before broadening the pilot.
Passing tests supports the specified behaviors under the tested assumptions. It does not prove abuse prevention, eliminate legitimate-user harm, or establish anonymity. Missing evidence should prevent expansion beyond the approved pilot scope.
Let AI tools assist with the work. Keep ownership, behavioral expectations, and release authority explicit.
Explore OpenThunder as you define your review policy.